End-of-Life Technology: Why Unsupported Hardware Threatens Network Security
For many organizations across Eugene, Springfield, and the broader Willamette Valley, technology budgeting tends to focus on visible needs. A new employee needs a laptop. The office WiFi feels slow. A server is running out of storage. Those items naturally make their way into budget discussions because the impact is easy to see.
What often gets overlooked is a quieter risk: technology that has reached the end of its supported life.
Unsupported hardware and software can remain operational for years after a manufacturer stops supporting it. Because it continues to function, leadership may assume it still presents little risk. Unfortunately, many cybersecurity incidents and operational disruptions involve systems that had been effectively abandoned by vendors long before anything actually broke.
The problem is not whether the technology still turns on. The problem is whether anyone is still responsible for keeping it secure.
What End-of-Life Really Means
When technology reaches end-of-life (EOL), the manufacturer has determined that the product will no longer receive updates, maintenance, bug fixes, or technical support.
This can apply to a wide range of business technology, including:
- Network switches
- Wireless access points
- Firewalls
- Servers
- Desktop computers
- Operating systems
- Specialized business equipment
- Industry-specific software platforms
Many organizations assume end-of-life means a device stops working. In reality, equipment may continue operating normally for months or even years.
For example, a wireless access point installed seven years ago may still provide internet connectivity throughout an office. Employees connect without issue, clients can access guest WiFi, and daily operations continue uninterrupted.
From a business perspective, everything appears fine.
From a security perspective, however, the device may no longer receive vulnerability patches, firmware updates, or manufacturer support. Any newly discovered weaknesses remain unaddressed indefinitely.
Recent discussions around aging WiFi infrastructure have highlighted this challenge. Organizations often begin considering replacement only after performance issues become noticeable. By that point, support deadlines may have already passed, creating both operational and security concerns.
The Security Impact Is Often Invisible
Cybersecurity discussions frequently focus on sophisticated threats, but unsupported technology creates a much simpler problem.
Attackers actively search for systems with known vulnerabilities.
When vendors release security updates for supported products, organizations can apply patches and reduce risk. When a product is no longer supported, newly discovered vulnerabilities often remain exposed permanently.
The Cybersecurity and Infrastructure Security Agency (CISA) consistently emphasizes the importance of maintaining supported technology because unpatched vulnerabilities remain one of the most common ways organizations are compromised.
For a small or midsize organization, unsupported systems can create several risks:
Increased Exposure to Security Incidents
Older devices may contain vulnerabilities that can never be corrected.
A firewall, wireless controller, or server that no longer receives updates may provide attackers with an easier path into the network than newer, supported systems.
Compliance Challenges
Healthcare practices, legal firms, financial organizations, and nonprofits handling sensitive client information often face regulatory or contractual obligations related to cybersecurity.
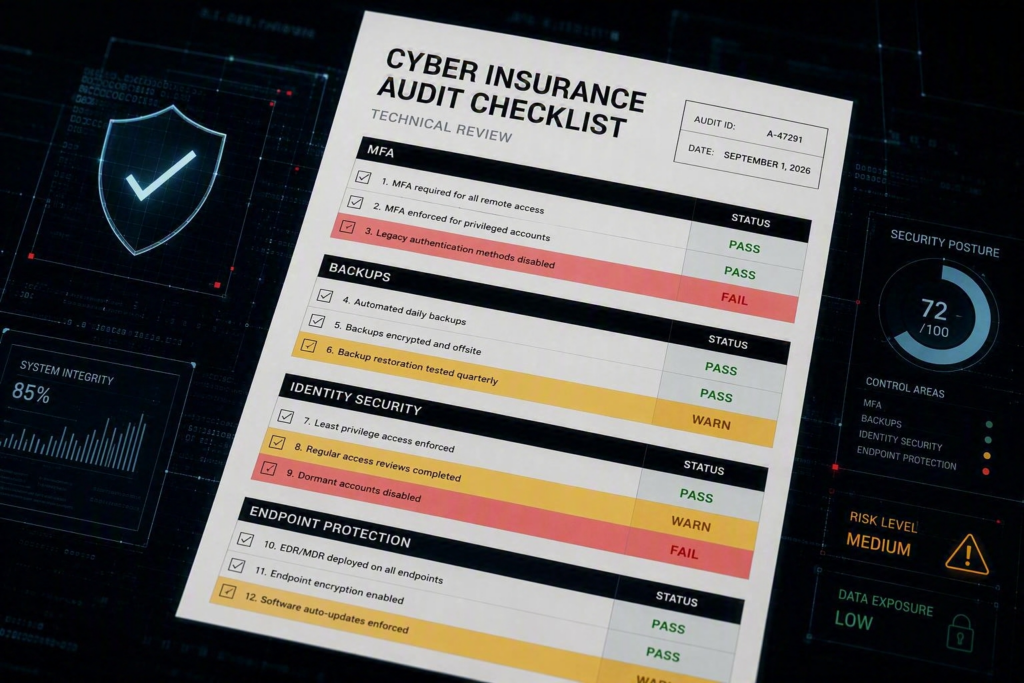
Using unsupported technology can complicate compliance efforts and raise questions during audits, security assessments, or insurance reviews.
Cyber Insurance Concerns
Insurance carriers increasingly examine cybersecurity practices during renewals and claims investigations.
Organizations may be asked to demonstrate that critical systems are supported and maintained. If aging infrastructure contributes to an incident, the resulting review process can become significantly more difficult.
Increased Downtime
Security is not the only concern.
Once support ends, replacement parts become harder to obtain and technical assistance becomes limited or unavailable.
A failure that might have been resolved quickly with supported equipment could instead lead to prolonged downtime, operational disruption, and unexpected expenses.
Understanding Vendor Support Timelines
Most technology products follow a predictable lifecycle.
Manufacturers typically announce:
- General availability
- End-of-sale dates
- End-of-support dates
- End-of-life deadlines
The challenge for many business leaders is that these announcements often occur years before support actually ends.
Unless someone is actively monitoring vendor communications, critical dates can easily be missed.
This issue is particularly common in organizations with lean internal IT resources. Technology deployments may occur during office expansions, renovations, or infrastructure upgrades and then receive little strategic attention afterward.
Seven or eight years later, equipment may still be operating but no longer supported.
This creates a dangerous gap between perceived reliability and actual risk.
A network may appear healthy while quietly accumulating unsupported components that no longer meet modern security standards.
Why End-of-Life Technology Creates Budget Problems
Technology replacement is often treated as an unexpected expense rather than a planned business investment.
This is rarely intentional.
Most organizations are balancing competing priorities such as staffing, facilities, client services, and growth initiatives. When budgets become tight, it is tempting to postpone upgrades that are not causing visible problems.
The result is that infrastructure eventually reaches the end of support all at once.
Instead of replacing equipment gradually, leadership faces a large, unexpected project involving multiple systems that require immediate attention.
This creates several business challenges:
- Larger capital expenditures
- Unplanned operational disruption
- Increased security exposure
- Reduced negotiating flexibility
- Compressed decision timelines
Organizations that maintain a lifecycle-based budgeting process generally avoid these issues because replacements are anticipated years in advance.
Rather than reacting to emergencies, they align technology investments with broader business planning.
A Better Approach: Lifecycle Strategy
The goal is not to replace technology prematurely.
The goal is to understand where critical systems sit within their support lifecycle and plan accordingly.
An effective lifecycle strategy typically includes:
Asset Visibility
Leadership should know what technology the organization owns, where it is deployed, who relies on it, and when support ends.
Without accurate documentation, end-of-life risks often remain hidden until a problem emerges.
Regular Infrastructure Reviews
Periodic assessments can identify equipment approaching support deadlines before those deadlines become operational concerns.
These reviews help organizations prioritize investments and avoid surprises.
Multi-Year Budget Planning
Technology is easier to manage when replacement costs are spread across several budget cycles.
A predictable refresh schedule allows leadership to align infrastructure investments with organizational goals rather than emergency circumstances.
Risk-Based Prioritization
Not every system requires immediate replacement.
Critical infrastructure that protects sensitive information or supports core business operations should generally receive attention first, while lower-risk systems can often follow a longer timeline.
Strategic IT Oversight
Technology planning is most effective when treated as an ongoing business function rather than a series of isolated projects.
This approach helps leadership understand future risks, upcoming costs, and emerging opportunities before they become urgent.
Looking Beyond Whether It Still Works
One of the most common assumptions in small and midsize organizations is that functioning technology must still be acceptable technology.
In reality, support status matters just as much as operational status.
A firewall can still pass traffic. A wireless access point can still provide connectivity. A server can still host applications. Yet each may represent increasing risk if vendor support has ended.
Business leaders do not need to become experts in support lifecycle management, but they should expect visibility into it. Understanding which systems are approaching end-of-life allows organizations to make informed decisions, budget responsibly, and reduce avoidable security exposure.
For organizations throughout Lane County and the Willamette Valley, this is increasingly becoming a governance issue rather than a technical one. The question is not whether aging technology exists. The question is whether leadership knows where it is, what risk it creates, and when it should be replaced.
Emerald Technology Group helps organizations assess infrastructure lifecycles, identify unsupported systems, and build practical technology roadmaps that align with business goals. Through strategic IT planning, cybersecurity assessments, network management, and ongoing support, organizations can address end-of-life risks before they become operational disruptions or security incidents. The most effective time to deal with unsupported technology is long before it demands attention on its own.
What to read next
Back to Blogs