Cyber Insurance Requirements for SMBs in 2026
For many business owners and operations leaders across Eugene, Springfield, and throughout Lane County, cyber insurance used to feel like a routine administrative task. A few forms, a handful of questions, and a renewal process that rarely required significant discussion.
That reality has changed.
Today, many organizations discover that cyber insurance applications have become something much closer to a cybersecurity assessment. Insurers increasingly want proof that key security controls exist, are actively managed, and are functioning as intended. What was once largely a paperwork exercise is now often a review of your organization’s ability to prevent, detect, and recover from cyber incidents.
For small and midsize businesses, that shift creates a new business risk. An incomplete application, unsupported security claim, or missing control can lead to higher premiums, coverage limitations, delayed renewals, or even denial of coverage. Understanding what insurers are evaluating before renewal season arrives can help leadership avoid unnecessary surprises.
Why Cyber Insurance Requirements Keep Evolving
Cybercrime continues to affect organizations of every size. Ransomware attacks, business email compromise, vendor account breaches, and credential theft remain common across nearly every industry.
As insurers have paid more claims and experienced larger losses, many have responded by increasing underwriting requirements. Rather than assuming applicants have adequate protections in place, insurers are asking more detailed questions about how organizations manage cybersecurity risk.
This trend affects law firms, nonprofits, healthcare practices, CPA firms, manufacturers, construction companies, and professional service organizations alike. Insurers increasingly recognize that an organization with 25 employees can experience many of the same cyber threats as an enterprise with thousands of employees.
For leadership teams, this means cyber insurance is becoming closely tied to operational maturity. Security controls that were once considered best practices are increasingly viewed as baseline requirements.
Common Security Controls Under Review
While requirements vary between carriers, several areas appear repeatedly in cyber insurance questionnaires.
Multi-Factor Authentication (MFA)
Multi-factor authentication remains one of the most commonly reviewed controls.
Insurers typically want to know whether MFA protects:
- Email accounts
- Remote access systems
- Administrative accounts
- Cloud applications
- Vendor and financial platforms
Many successful cyber incidents still begin with stolen credentials. MFA helps reduce the likelihood that a compromised password alone can lead to unauthorized access.
Leadership should also understand that insurers increasingly distinguish between partial MFA deployment and organization-wide MFA enforcement. Having MFA available is different from requiring it consistently.
Endpoint Protection
Questions about computers, laptops, and servers have also become more detailed.
Insurers often inquire about:
- Endpoint detection and response capabilities
- Antivirus or anti-malware protections
- Device monitoring
- Patch management practices
- Security management oversight
The goal is straightforward. If a device becomes compromised, insurers want confidence that the organization can detect suspicious activity and respond before a problem spreads across the business.
Vulnerability and Risk Management
Many questionnaires now include questions about security assessments, vulnerability reviews, and remediation procedures.
The focus is often less about achieving perfection and more about demonstrating that the organization has a defined process for identifying and addressing cybersecurity risks over time.
Organizations that can document regular oversight often present a stronger risk profile than those relying on assumptions or informal practices.
Backup Proof Versus Backup Assumptions
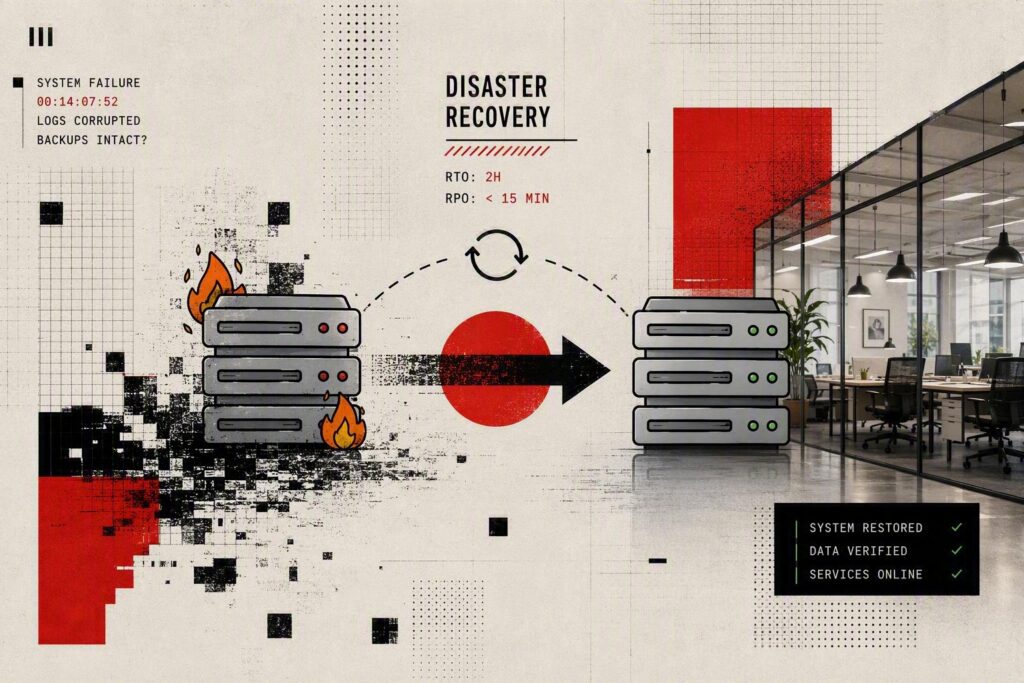
One of the most important shifts in cyber insurance underwriting involves backup validation.
Many businesses confidently state that backups exist because no one has reported a problem. Unfortunately, an untested backup may not provide meaningful protection during an actual incident.
Insurers increasingly want evidence that organizations understand:
- What data is being backed up
- How frequently backups occur
- Whether backups are protected from ransomware
- How recovery procedures are tested
- How long restoration would realistically take
The distinction between having backups and being able to recover from backups is significant.
A ransomware event can quickly expose weaknesses that went unnoticed for years. Missing data, failed backup jobs, incomplete coverage, or recovery delays can create substantial operational disruption.
For a healthcare practice, that disruption could affect patient scheduling. For a CPA firm, it could interrupt tax deadlines. For a law firm, it could impact client service obligations. For a nonprofit, it could disrupt donor operations and financial management.
The organizations that perform regular backup validation tend to have far greater confidence during an insurance renewal review because they can demonstrate actual resilience rather than assumed resilience.
Identity Security Expectations Continue to Rise
Identity has become one of the most important cybersecurity concerns for insurers.
The modern workplace relies on numerous cloud applications, vendor portals, financial systems, remote access platforms, and collaboration tools. Each account represents a potential entry point for attackers.
As a result, insurers increasingly examine how organizations manage user identities and access rights.
Areas commonly reviewed include:
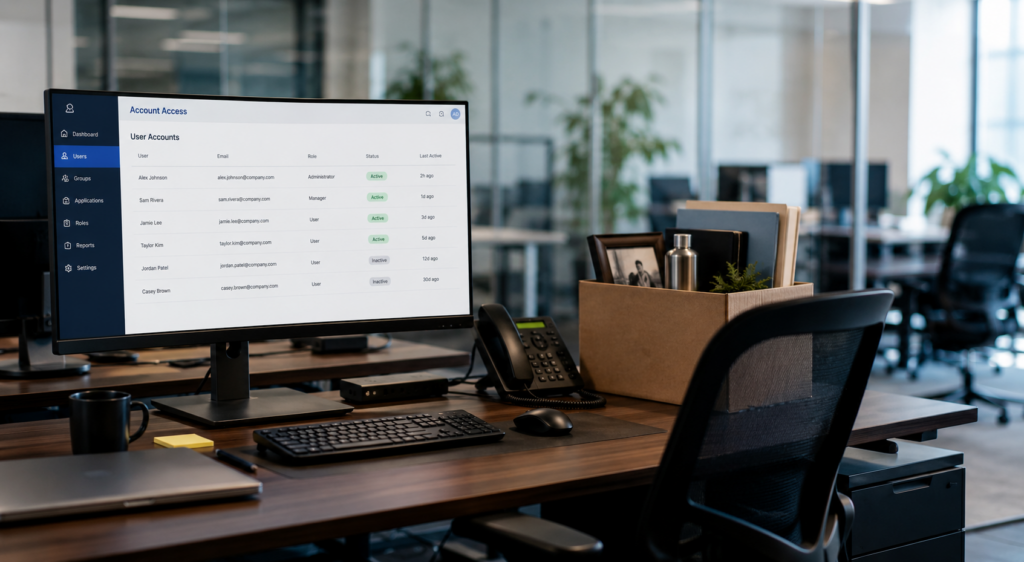
Account Management
Organizations should know:
- Who has access to critical systems
- Which accounts have administrative privileges
- Whether former employees have been removed promptly
- How access approvals are documented
Privileged Access
Administrative privileges often receive special attention because compromised administrator accounts can have widespread impact.
Insurers increasingly expect organizations to limit elevated privileges and manage them carefully rather than granting broad administrative rights across the organization.
Shared Credentials
Shared usernames and passwords remain common within smaller organizations, but they create both security and accountability challenges.
Many insurers view individual accountability for system access as an important component of cybersecurity governance.
For leadership teams, identity security is ultimately about visibility and control. If an organization cannot clearly identify who has access to critical systems, it becomes much more difficult to manage risk effectively.
Preparing Before Renewal Season
One of the biggest mistakes organizations make is waiting until the renewal questionnaire arrives before evaluating their security posture.
By that point, there may be limited time to close gaps, gather documentation, or validate security claims.
Instead, organizations should prepare several months before renewal by reviewing key controls, documenting procedures, and identifying areas that may require improvement.
Practical preparation often includes:
- Reviewing MFA deployment and enforcement
- Validating backup and recovery processes
- Confirming endpoint protection coverage
- Reviewing administrative account access
- Conducting a cybersecurity assessment
- Updating incident response documentation
- Verifying employee onboarding and offboarding procedures
- Identifying gaps that could raise underwriting concerns
This preparation is not simply about satisfying an insurer. The same controls insurers evaluate often support business continuity, operational resilience, regulatory compliance, and client trust.
A stronger renewal process is frequently the byproduct of stronger risk management.
Cyber insurance remains an important component of business protection, but insurers increasingly expect organizations to demonstrate that they are actively managing cybersecurity risks rather than transferring responsibility through a policy alone.
Business leaders should view upcoming renewals as an opportunity to evaluate whether their current security practices align with today’s expectations. Understanding what insurers are looking for before the questionnaire arrives allows organizations to address gaps proactively and avoid unnecessary renewal challenges.
For many small and midsize organizations throughout the Willamette Valley, that preparation benefits from an outside perspective. Emerald Technology Group helps businesses assess cybersecurity risk, validate critical controls, review backup and disaster recovery readiness, and align managed IT and security practices with evolving insurance expectations. The goal is not simply obtaining coverage, but ensuring the organization is prepared to withstand the incidents that coverage is intended to address.
What to read next
Back to Blogs