Why Backup Success Does Not Guarantee Disaster Recovery
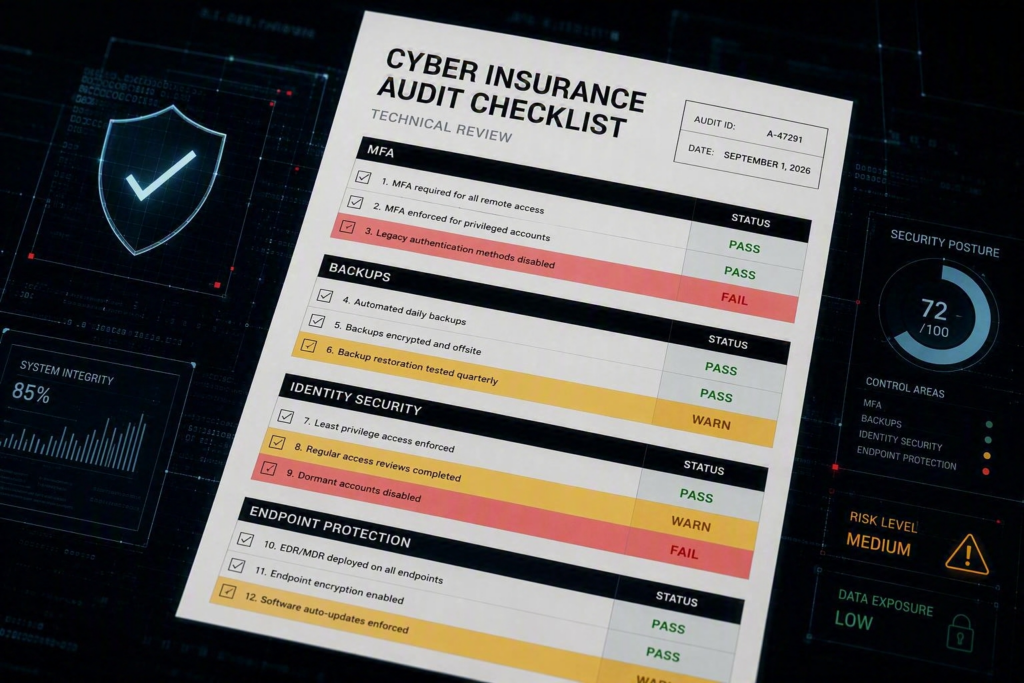
For many organizations, backup success reports create a sense of reassurance. Data was copied. Jobs completed successfully. Storage systems are functioning. On paper, everything looks fine.
But there is a growing realization across businesses in Eugene, Springfield, and throughout Lane County that successful backups do not necessarily mean successful recovery.
A backup is a technical process. Recovery is a business outcome.
When a cyberattack, system failure, natural disaster, or major vendor outage occurs, leadership is not asking whether the backup completed at 2:00 a.m. They are asking when employees can get back to work, when clients can be served again, and how much disruption the organization faces.
That distinction is driving a significant shift in how organizations measure resilience. Increasingly, recovery readiness is replacing backup completion as the metric that matters most.
Backup and Recovery Are Not the Same Thing
Many businesses assume that if their backup system is functioning properly, they are protected.
Unfortunately, that assumption often goes untested.
Backup systems are designed to preserve data. Disaster recovery focuses on restoring business operations. Those are related objectives, but they are not identical.
A company may have perfectly healthy backups and still discover critical challenges when attempting to restore operations:
- Applications may not reinstall properly.
- Configuration settings may be missing.
- User permissions may not transfer correctly.
- Network connectivity may fail.
- Authentication systems may not be available.
- Third-party integrations may no longer work.
The result is a situation where data exists but productivity remains stalled.
This reality has become especially important as ransomware recovery incidents increase. Organizations frequently learn that restoring data is only one step in a much larger recovery process.
Business continuity depends on restoring the entire operating environment, not merely recovering files.
Recovery Time Expectations Must Match Business Reality
One of the most common gaps in resilience planning involves assumptions about recovery speed.
Leadership teams often assume critical systems can be restored quickly because backup technology is modern and reliable. In practice, recovery can take significantly longer than expected.
Consider a law firm preparing for a court filing deadline, a CPA firm approaching tax season, or a healthcare practice managing patient appointments. Even a short disruption may create substantial operational consequences.
Every organization should clearly answer questions such as:
- How long can we operate without our primary line-of-business application?
- How long can email remain unavailable?
- How many hours of lost data would be acceptable?
- Which systems must be restored first?
- Which departments are most sensitive to downtime?
These questions define business recovery objectives.
Without documented recovery expectations, organizations often discover during a crisis that their assumptions and technical capabilities do not align.
The purpose of recovery planning is not to eliminate downtime entirely. It is to ensure leadership understands what recovery will realistically look like before an emergency occurs.
Application Dependencies Often Create Hidden Risks
Modern businesses rely on far more than files and servers.
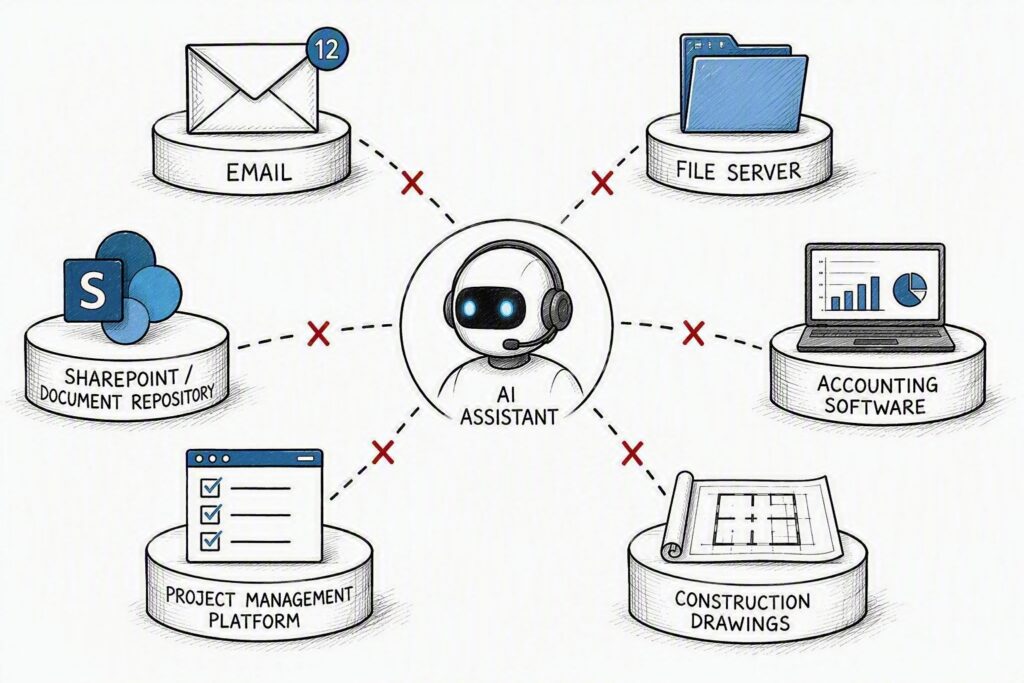
Most organizations depend on a complex ecosystem of applications, cloud platforms, authentication services, industry software, and third-party integrations. Many of these dependencies are invisible until something breaks.
For example, a construction company may depend on project management platforms, estimating software, accounting systems, mobile field applications, and document storage services.
A nonprofit may rely on donor management systems, financial software, volunteer databases, and communication platforms.
A healthcare practice may depend on electronic health records, scheduling systems, patient portals, and external compliance services.
Recovering one application does not necessarily restore all the systems surrounding it.
This is why effective disaster recovery planning includes dependency mapping. Organizations should identify:
- Which applications support critical business functions.
- Which systems must be restored first.
- Which applications depend on other services.
- Which cloud resources are required for operations.
- Which user groups need priority access during recovery.
Many recovery failures are not caused by missing backups. They occur because organizations did not fully understand how business processes depended on interconnected systems.
Vendor Dependencies Deserve More Attention
Business recovery increasingly depends on external vendors.
Even organizations with strong internal IT capabilities may find themselves waiting on software providers, cloud platforms, internet providers, cybersecurity vendors, or industry-specific service providers during an outage.
If a critical vendor experiences downtime, a security incident, or service disruption, your organization may have little direct control over the outcome.
This risk is particularly relevant for organizations that have embraced cloud-based operations. While cloud services often improve reliability, they also create dependencies that should be evaluated as part of business continuity planning.
Leadership should periodically review questions such as:
- Who are our most critical technology vendors?
- What recovery commitments have they made?
- Do we understand their service-level expectations?
- How would we operate if a vendor became unavailable?
- Do we have alternative processes during an outage?
Vendor management is increasingly becoming a cornerstone of business resilience.
A recovery plan that ignores third-party dependencies may leave critical gaps exposed when an actual disruption occurs.
Annual Recovery Testing Should Be a Leadership Exercise
Many organizations test backups.
Far fewer test recovery.
Even fewer conduct full-scale recovery exercises that involve both technology teams and business leadership.
Annual recovery testing should examine the business process as a whole, not simply confirm that files can be restored.
A meaningful recovery exercise should address questions such as:
- Can critical systems be restored within expected timeframes?
- Do employees know their responsibilities during an incident?
- Are emergency contacts current?
- Are vendor escalation procedures documented?
- Can business operations continue using alternate workflows?
- Are communication plans established for staff, clients, and stakeholders?
The objective is not to achieve perfection.
The objective is to identify weaknesses before a real event exposes them.
Organizations routinely conduct fire drills, safety exercises, and financial audits because testing reveals important gaps. Recovery planning deserves the same level of attention.
Business leaders who participate in recovery testing gain a much clearer understanding of operational risk, resource requirements, and recovery expectations.
Recovery Readiness Is the New Resilience Metric
The most resilient organizations no longer measure success solely by whether backups completed successfully.
Instead, they ask a more important question:
“If we lost critical systems tomorrow, how confidently could we restore business operations?”
That shift changes the conversation from technology performance to organizational resilience.
For small and midsize organizations throughout the Willamette Valley, recovery readiness requires understanding business priorities, documenting dependencies, validating vendor relationships, and regularly testing assumptions.
A successful backup remains an important part of the equation. However, resilience is ultimately measured by how effectively the organization can continue serving clients, supporting employees, and fulfilling its obligations when unexpected disruptions occur.
Business leaders should review recovery plans annually, involve both operational and technical stakeholders in testing exercises, and ensure recovery objectives reflect current business realities. Emerald Technology Group works with organizations across Eugene, Springfield, and Lane County to assess recovery preparedness, identify operational dependencies, and develop practical business continuity strategies that support long-term resilience and responsible IT management.
What to read next
Back to Blogs